AI Governance & Compliance
Know where AI is used in your company, what the rules ask of each use, and have the documents and controls to show it.
Most companies already use AI in more places than anyone has written down: a chatbot on the website, a model inside a vendor’s product, staff pasting customer data into an assistant. Regulators, customers and insurers are starting to ask about all of it. The EU AI Act reaches companies outside the EU when their AI is used there, and privacy laws such as GDPR, PIPEDA and Quebec’s Law 25 already apply to the personal data AI runs on, and some of them to automated decisions about people.
We are engineers, so we start from what your systems actually do. We map every place AI touches your data and your customers, sort each use by risk, and put in place the controls, documentation and training the rules call for. We work alongside your lawyer, not instead of one: our part is making the technical side true and provable.
What we take on
AI inventory and risk classification
A register of every AI system you build, buy or let staff use, sorted by the EU AI Act’s risk levels and by the personal data each one touches.
AI policy and governance
An acceptable-use policy people can follow, a named owner for each system, and an approval step before new AI tools come in.
Impact assessments and documentation
Privacy and algorithmic impact assessments, model and data documentation, and the records a customer, auditor or regulator will ask for.
Transparency and disclosures
Telling people when they are talking to a bot or looking at generated content, and the AI disclosures that app stores and marketplaces now require.
Controls in the software itself
Logging, human review where it matters, data minimisation, accuracy and bias testing, and keeping personal data on the device when that is enough.
Vendor and model due diligence
What your AI suppliers do with your data, where it is processed, and what their terms allow them to train on.
How an engagement runs
Scope
A conversation, then a short written plan: what gets done first, what it costs, and what is deliberately left out.
Build
Working results early and often. You see progress in something running, not in status reports.
Ship
Deployment, monitoring and backups are part of the job, not an afterthought.
Hand over
Your code, your accounts, and documentation written for whoever maintains it next.
Frameworks we work to
Work that backs this up
Our own apps carry the disclosures and privacy design this work is about: AI labels on their store listings, and models that keep photos on the phone.
PlantSync
Houseplants with personalities
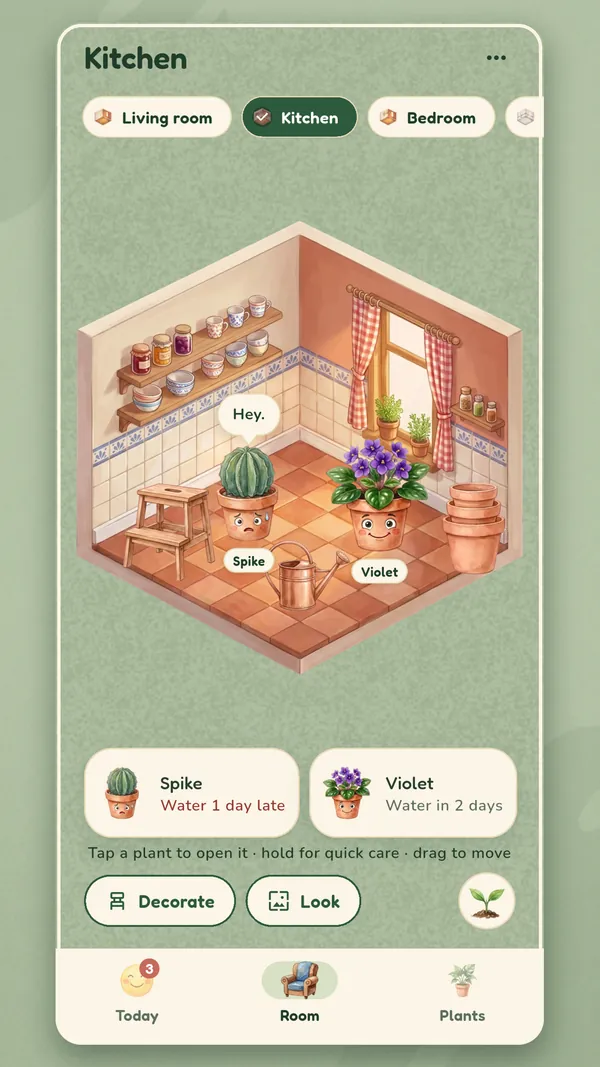
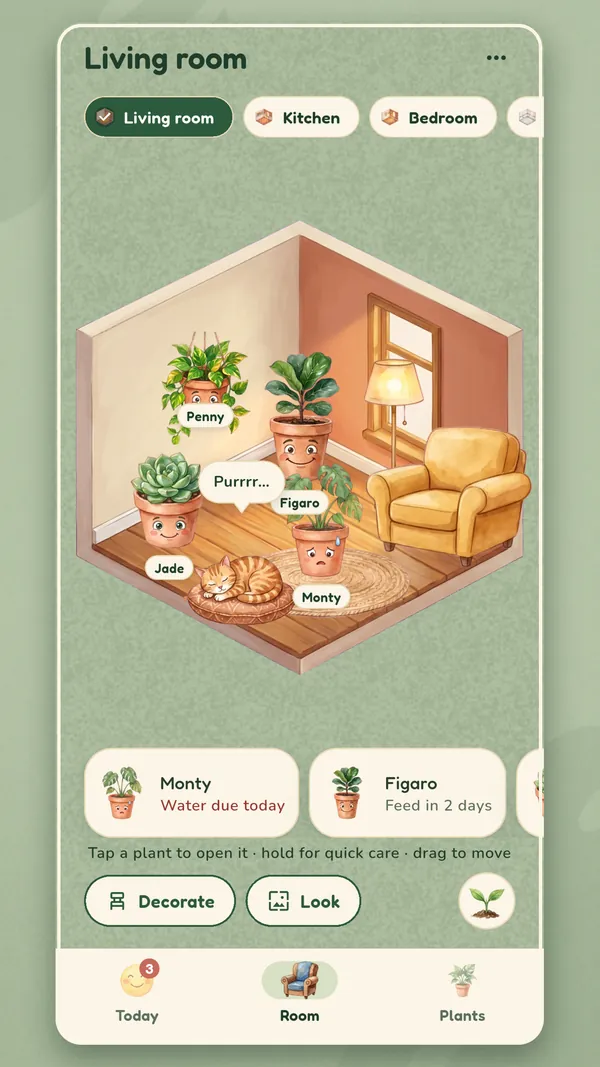
Every plant you own moves into a little room you furnish and decorate. They chat, they have moods, and they play mini-games with you, and the app still tells you when the real one needs water.
Pletto
Colouring and drawing for ages 2 to 6
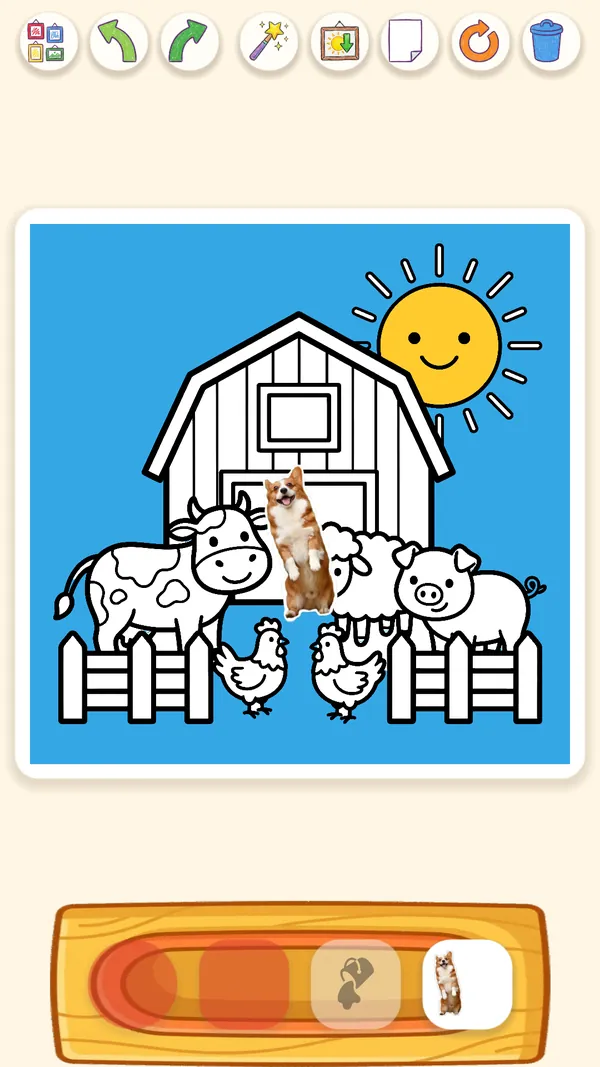
A colouring book for the youngest hands: pages that fill with a tap, free drawing, stickers of their own photos and crafts to print. No ads, no accounts, and nothing ever leaves the device.
Questions we get asked
Does the EU AI Act apply to a company outside the EU?
It can. It covers companies that put AI systems on the EU market, and companies whose AI produces output that is used in the EU, wherever they are based. A Canadian or US company that sells software or services into Europe should check where it stands.
We only use ChatGPT and a few SaaS tools. Do we need this?
Probably a light version of it. For a small company most of the work is knowing which tools people use with which data, a short policy, and checking what your vendors do with that data. We size the work to the company.
Can you get us ISO/IEC 42001 certified?
We can set up the AI management system the standard describes and get you ready for the audit. The certificate itself is issued by an accredited certification body after its own audit.
Is this legal advice?
No. We handle the technical and operational side: what your systems do, the documentation, and the controls in the software. Questions of legal interpretation belong with your lawyer, and we are glad to work alongside them.
Further reading
Does the EU AI Act apply to Canadian and US companies?
The EU AI Act reaches companies outside Europe when their AI is used there. Who it covers, the dates after the 2026 Digital Omnibus, and what to do first.
An AI compliance checklist for small and mid-sized companies
Ten practical steps to get AI use under control: an inventory, a short policy, vendor checks, disclosures and records, for a company without a compliance team.
Keeping the photo on the phone: on-device AI in three of our products
How PlantSync, Pletto and Inventyl run their image models on the device instead of in the cloud, what that costs, and when it is the right call.